01
Context
Limit the inputs
Give the agent the relevant folder or documents rather than everything on your desktop.
Looking up a price, filling in a form, and submitting it are different actions. Tell Think-Act where to stop, and check the tool permissions that determine whether an action proceeds, asks for approval, or is blocked.
Windows 10 and 11 now. Mac release planned.
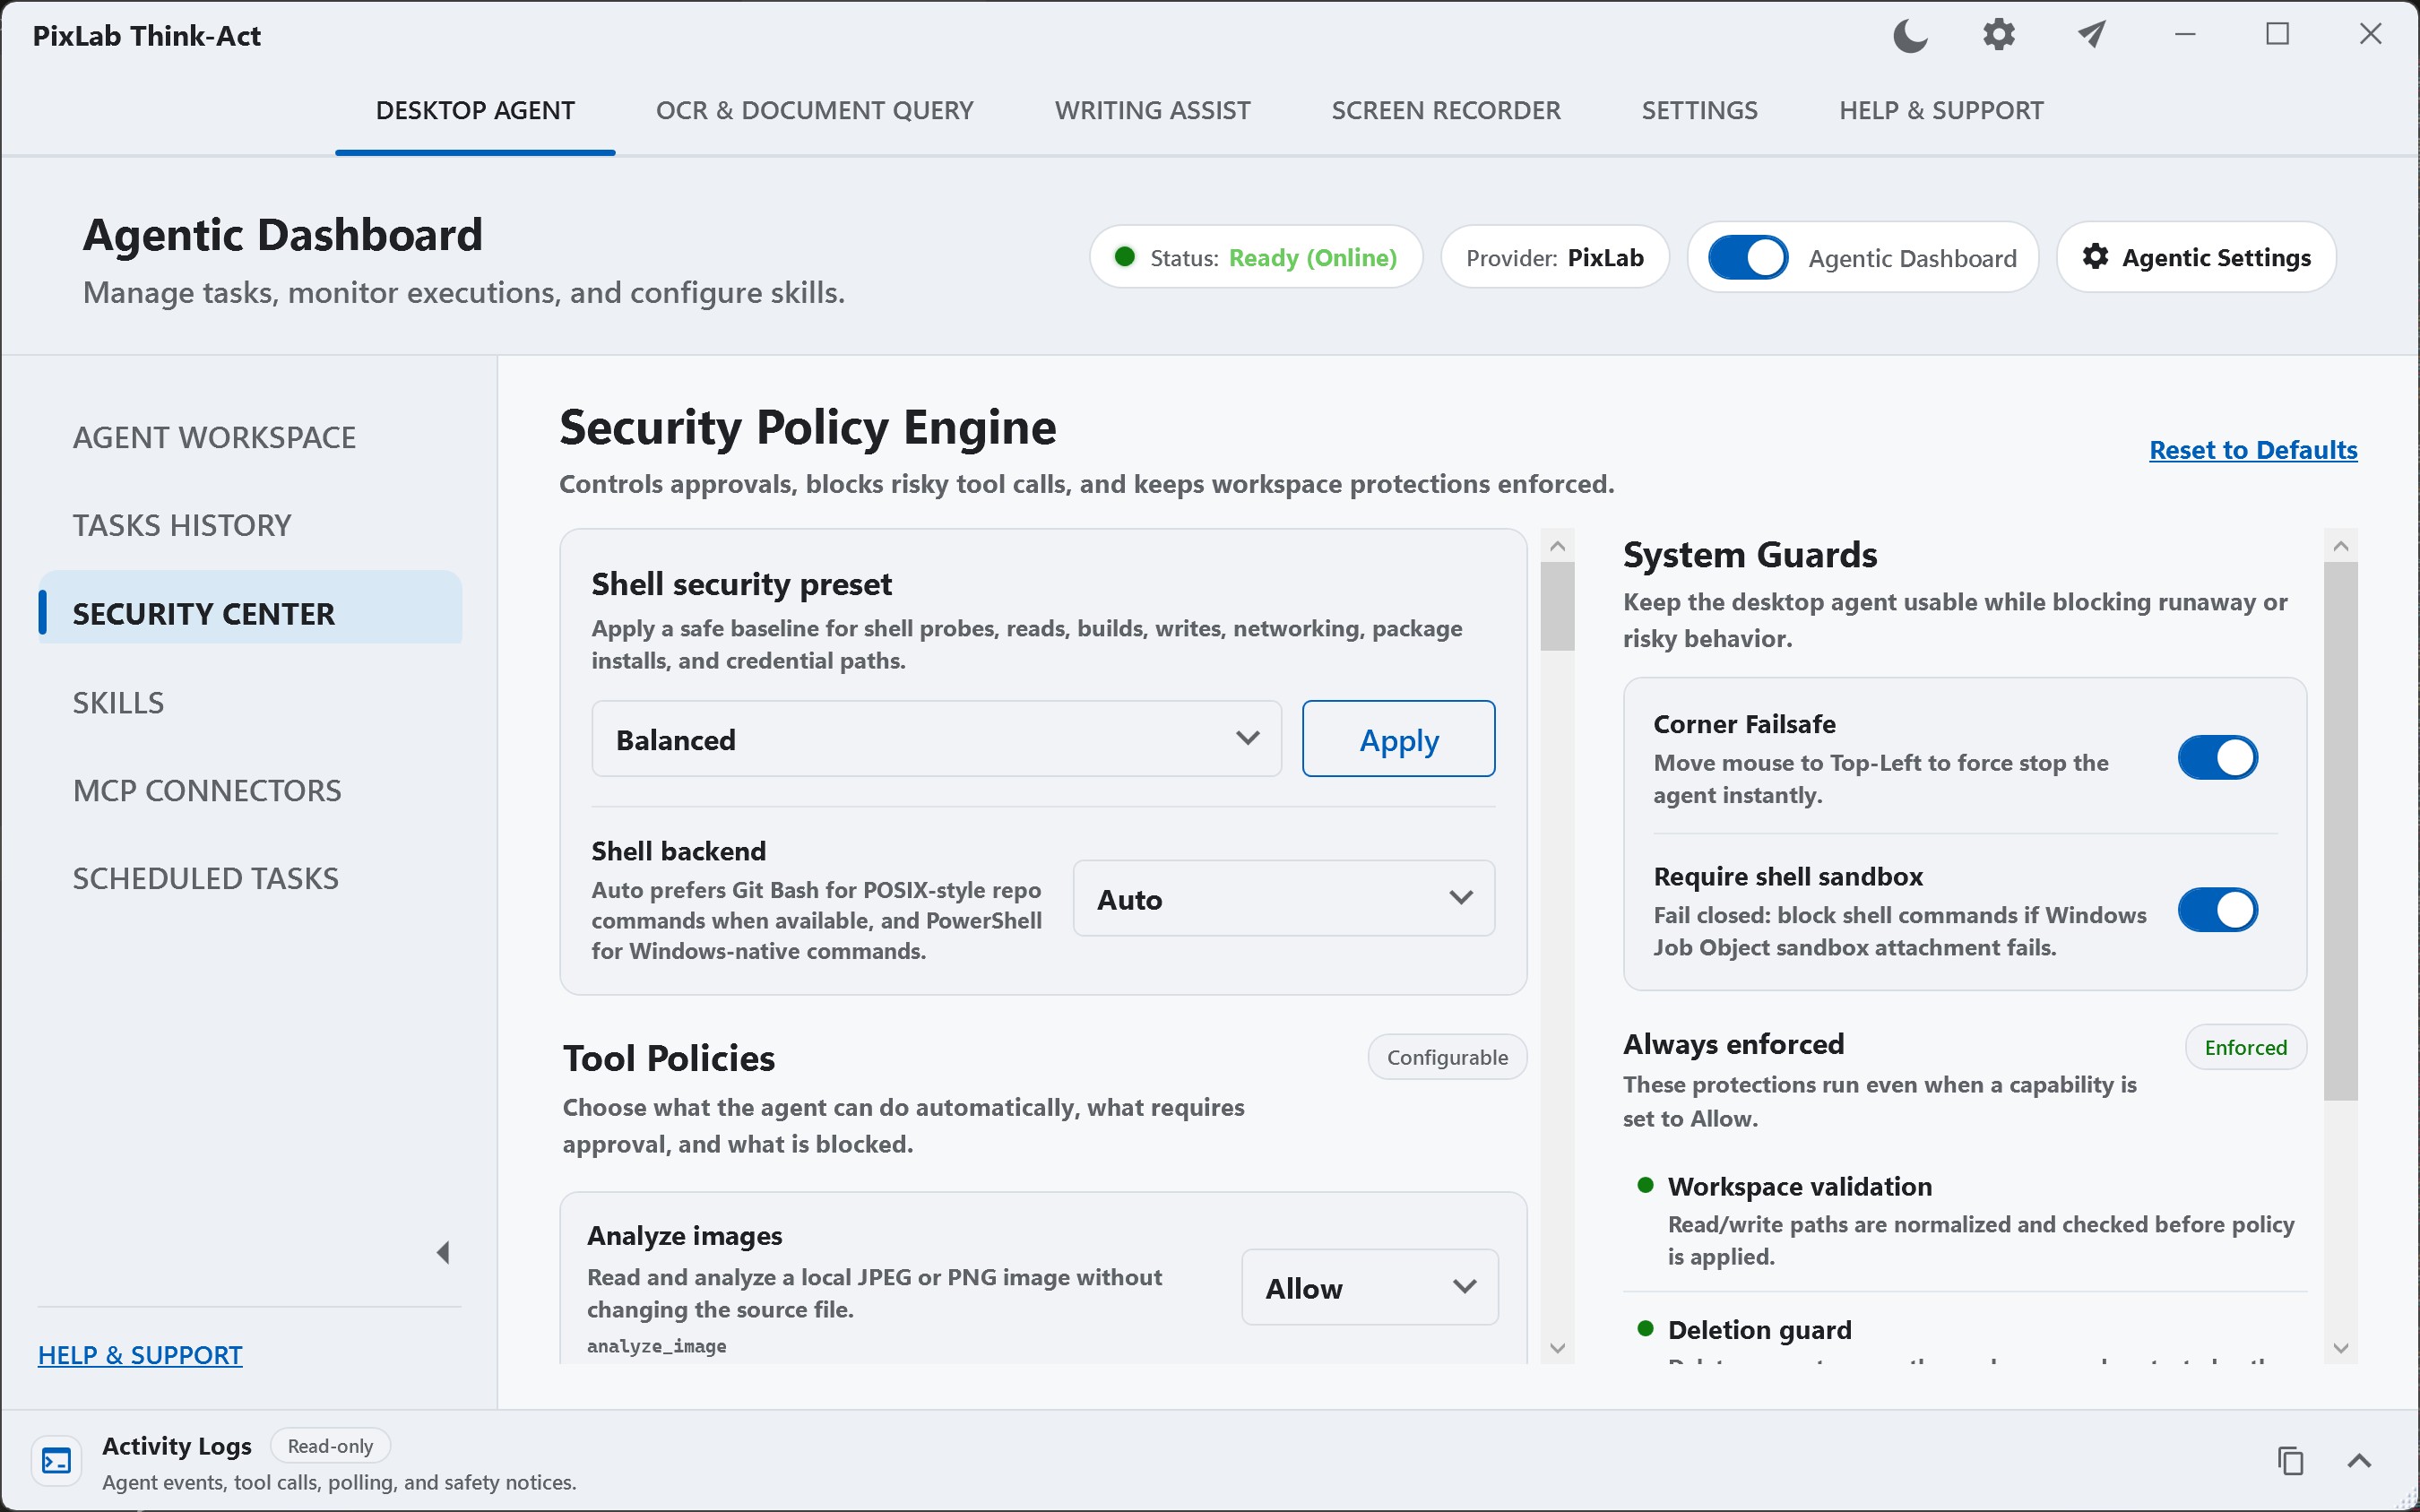
Controlled task workflow
The app runs on your desktop. A cloud model or connected service may receive the text, images, or files needed for a request.
Context
Give the agent the relevant folder or documents rather than everything on your desktop.
Think-Act
Ask for a list of proposed renames first if you want to check them before editing files.
Service
A local app can still send text to a model provider or a connector. Check both before supplying private data.
Review
Open the resulting file. If the agent changed a website or another app, check the change there as well.
The key point: running Think-Act locally does not mean every service involved in a workflow also runs locally.
Allowed actions can run without a prompt. Ask waits for you; Block prevents the action.
The goal is deliberate access, not friction everywhere
Low-impact work can stay simple. Actions with meaningful side effects deserve more scrutiny while a workflow is being understood and tested.
Capability
Keep the run tied to supported tools, Skills, and connectors that are actually configured and available to the task.
Permission
For supported actions, Think-Act can follow configured ALLOW, ASK, or BLOCK policy. Match the policy to the action and its consequences.
Review
Review the final output together with relevant supported activity, tool use, observations, confirmations, or reported changes. Treat this as review evidence, not a complete audit trail.
External trust
Third-party MCP packages, model endpoints, runtimes, accounts, and connected services bring their own behavior and data-handling rules. Review them independently before relying on the workflow.
Permission is action-specific
Do not assume every connector exposes one identical permission surface. Use the controls supported by the capability you are configuring.
A read-only comparison doesn’t need permission to change a business record. Start with the smaller scope.
Allow
Useful when the scope and consequence are understood and an approval pause is not required.
Ask
A practical starting point for write, send, publish, delete, or other consequential actions while testing a workflow.
Block
Use when the action does not belong in the task or its consequence is not acceptable.
Disable or leave out connectors the task does not require where appropriate.
Increase autonomy only after you understand the action, its expected side effects, and how you will verify success.
A Skill preserves reusable guidance. It does not create a connector, bypass missing capability, or override the workflow's permission boundary.
Check the publisher and what the package can access. Running locally is not a guarantee of trust.
Third-party MCP packages are not automatically trusted
Third-party MCP packages are not controlled or audited by PixLab unless explicitly stated. Think-Act's workflow permission model does not replace the operating-system permissions or security properties of the package itself.
Read the filename, destination, or requested action. Pausing a task doesn’t reverse a change that has already happened.
Completion is not proof
Compare important claims, values, extracted details, file changes, or external effects with the source and the outcome you expected.
Request
The workflow can only rely on supported capabilities that are actually available to the task.
Review / decide
Inspect the requested action and consequence, then approve or deny it deliberately instead of treating confirmation as a routine click-through.
Inspect
Use relevant supported activity, observations, confirmations, or reported changes to understand how the workflow reached its result. This is review evidence, not full chain-of-thought visibility.
Recover / reuse
Use supported checkpoints or recovery controls where they apply. External actions may not always be reversible, so do not treat recovery as universal undo.
Turn a workflow into a reusable Skill only after the prerequisites, access, expected result, and review checks are understood.
Saved instructions can standardize a task, but they don’t change tool access or waive your permission rules.
Important controls, dialogs, approvals, and navigation should remain usable without requiring precise pointer input.
Actions should explain what they do so users can distinguish approval, cancellation, review, retry, and other choices.
Text, controls, focus indicators, and important state changes should remain distinguishable across light and dark interfaces.
A warning should identify the issue and help explain why an action is blocked, risky, unavailable, or requires confirmation.
More than color
Approved, blocked, unavailable, warning, and error states should combine meaningful text, recognizable icons, clear labels, and sufficient visual contrast rather than relying on blue, green, amber, or red alone.
Check the settings available in your build. Ask PixLab about organization-wide controls rather than assuming they come with a plan.
Planned / roadmap
Broader managed integration concepts may include cloud connector discovery, organization-level policies or provisioning, and remote-agent integration ideas.
Find out when an approval appears and how local and external tools handle data.
No. MCP packages can run code with the permissions of the process. Use only packages from sources you trust.
No. Local files can still be sent to a configured model or connector when needed for a task. Check those destinations before sharing private data.
The existing security policy considers the requested tool and action. It can allow it, ask you to confirm it, or block it.
No. Reusable instructions do not grant permissions, bypass blocked actions, or install missing tools.
Inspect the failed step. Enable the right trusted connector or choose a result that doesn't need it.
No. Web research and hosted models require a connection. Local processing depends on your configured provider and tools.
Open the task's activity log and the resulting files. If the job changed another app, check the result there as well.
The app has action approvals, protected paths, and tool activity records. Don't assume a centralized enterprise policy or audit dashboard is included.
Ask the agent to check the free space on your drives. Inspect the tool activity before giving it a job that changes files.